GDPR for AI BDSM Chats: 2026 Guide
GDPR for AI BDSM Chats: 2026 Guide
Before I share intimate details with an AI chat service, I check three things: consent, storage, and deletion. Chats that reveal sex life or sexual orientation can fall under GDPR’s special-category rules. Agreeing to role-play is not permission to use those chats for model training.
In this guide, I explain what to check:
- Data use: Separate account details from intimate chats, and check the legal basis for each use.
- Consent and age checks: Look for explicit consent, separate choices for optional uses, and adult verification that limits ID collection.
- Storage and access: Review chat history, memory, training, vendor access, and transfers outside the EEA.
- Privacy safeguards: Check retention limits, security measures, risk reviews, and breach plans.
- Your rights: Find controls for access, correction, deletion, and consent withdrawal. Rights requests generally require a response within one month.
I also explain when GDPR can apply to a service outside Europe, including a US operator. My starting rule: <u>check what happens to your data - not just where the servers sit.</u>
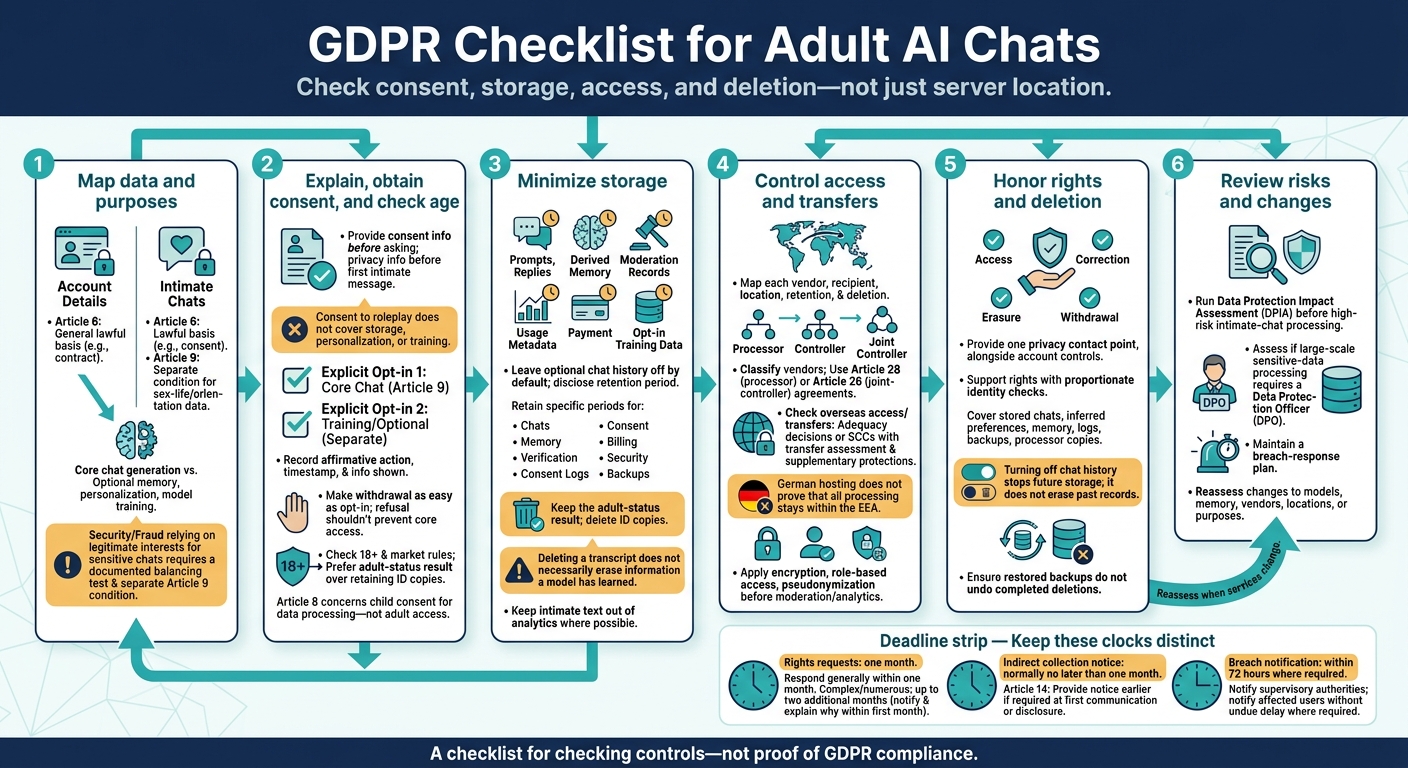
GDPR Checklist for Adult AI Chats
Lawful Bases, Consent, and Age Checks
Map Each Data Use to a Lawful Basis
For each AI chat purpose, identify the data needed and the lawful basis for using it. Article 6 provides the general lawful basis. Article 9 requires a separate condition for sex-life or sexual-orientation data. Legitimate interests may support security and fraud prevention, but only after a documented balancing test.
Use this matrix to distinguish required processing from optional uses.
| Purpose | Possible Article 6 basis | Article 9 assessment | Records to keep |
|---|---|---|---|
| Account creation and login | Contract | Not usually needed for account data | Terms of service acceptance |
| Explicit chat generation | Contract, where needed to provide the service | Explicit consent | Specific affirmative consent record |
| Age verification | Legal obligation, where applicable | Required if biometric data is used for unique identification | Verification method and result |
| Security, fraud prevention, and chat moderation | Legitimate interests | Separate condition needed if sensitive chat data is processed | Legitimate interest assessment |
| Optional chat memory and personalization | Consent | Explicit consent if sensitive data is involved | Opt-in and withdrawal records |
| Optional model training | Consent | Explicit consent if sensitive data is involved | Opt-in and withdrawal records |
Get Explicit Consent for Sensitive Data
Consent to roleplay does not cover storage, personalization, or training. Keep optional storage, memory, personalization, and training separate from core access. Give users clear, separate opt-in controls, and record their affirmative action, its timestamp, and the information they saw. Consent must be informed, specific, freely given, and unambiguous. For sensitive data, it must also be explicit.
Users who refuse training or advertising should still be able to use the core service. Make withdrawal as easy as opting in. Once users withdraw, stop the affected processing and delete their data unless a lawful retention exception applies. Consent does not permit unnecessary collection or indefinite storage.
Verify Adult Access With Less Personal Data
Once consent rules are in place, verify adult access using as little personal data as possible. Article 8 covers child consent for data processing - not adult access. Check each market’s rules before selecting a verification method, and prefer a minimum-age result over stored ID copies.
| Method | Assurance | Data collected | Privacy risk | Deletion approach |
|---|---|---|---|---|
| Age declaration | Low | Minimal, self-reported | Low | Immediate |
| Age estimation | Medium | Face or voice data | Moderate | Delete after estimation |
| Digital identity check | High | Third-party token | Low for the service | No ID data retained |
| Document verification | Very high | Full ID scan | High | Immediate purge required |
Block underage users and purge their data. Give adults who fail an automated check an appeal route and another suitable verification method. Keep only narrowly justified records required for legal or security purposes.
sbb-itb-97c8eab
Chat Storage, Vendors, and Security
Limit Chat History, Memory, and Model Training
After establishing a lawful basis and obtaining consent, check what the service stores, who can access it, and for how long. Encryption and hosting location alone do not satisfy GDPR. Verify which chat data, identifiers, and logs remain after each session, and disclose any retained preferences, IP addresses, and device identifiers.
If the service offers chat history, leave it off by default and state how long it retains that history. Remove identifiers before moderation or analytics, and keep intimate text out of analytics where possible. Deleting a source transcript does not necessarily erase information a model has learned.
Manage Vendor Access and International Transfers
With storage limits in place, map every vendor and cross-border transfer. Classify each vendor as a processor, controller, or joint controller, and use the matching GDPR agreement. Apply Article 28 processor agreements or Article 26 joint-controller arrangements where appropriate. Require confidentiality, oversight of subprocessors, support for deletion, and limits on human review.
German hosting does not prove that all processing stays within the EEA. Identify overseas access and transfers. Then check applicable adequacy decisions or use standard contractual clauses, along with the required transfer assessment and supplementary protections.
Document each verified data flow before making privacy claims. Keep a verified data-flow register that records each data type, recipient, location, retention period, and deletion method. Cover prompts, replies, saved history, derived memory, moderation records, usage metadata, payment information, and opt-in training data. Use these same records to support incident response and breach notification.
Assess Privacy Risks and Plan for Breaches
Run a DPIA before processing intimate BDSM chats. Recommended safeguards include encryption in transit and at rest, role-based access controls, and pseudonymization before moderation or analytics. Prepare an incident response plan that covers notifications to supervisory authorities and users.
User Rights, Retention, and Privacy Notices
Respond to Rights Requests and Consent Withdrawal
Once you’ve limited storage and vendor access, explain how users can access or delete the data you keep and withdraw consent. Provide one privacy contact point alongside account controls for access, correction, erasure, and withdrawal. These options should cover stored chats and inferred preference profiles - not just account details - and include memory, logs, and backups.
Verify identity through a logged-in session or another check that fits the request. Ask for more information if you have reasonable doubts about the person’s identity.
| Right | Request channel | Proportionate identity verification | Notes |
|---|---|---|---|
| Access and correction | Account controls or privacy contact point | Logged-in access when sufficient | Return relevant data and correct inaccurate preferences. |
| Erasure | Delete control or privacy contact point | Confirm account ownership | Delete account and chat data, keeping only required legal, security, or billing records. |
| Consent withdrawal | Consent settings or privacy contact point | Logged-in access when sufficient | Stop future processing based on that consent. Turning off chat history stops future storage; it does not erase past records. |
GDPR allows up to two additional months for complex or numerous requests. Notify the user and explain the reasons within the first month. Include copies held by processors in your response workflow. History toggles control storage; they don’t confirm deletion.
Set Retention Periods for Each Purpose
Set purpose-specific retention periods for intimate chats, memory, age-verification records, consent logs, billing records, and backups. Give security logs their own justified schedule, retain billing records to meet accounting obligations, and keep age-verification evidence only as long as its stated purpose requires. Keep the adult-status result; delete ID copies.
Automate expiration, limit the scope of legal holds, and document why you need to retain each item. Restrict backup access and set backup expiration dates. Make sure restoring a backup doesn’t undo completed deletions.
Explain what, if anything, remains after account deletion. Pseudonymized records still count as personal data when they can be linked back to a person.
Explain Data Uses Before Collection
Before the first intimate message, tell users what you collect, why, and how they can control it. Start with a short notice and provide more detail in the privacy notice.
State the operator’s location and contact details. Use plain language to explain purposes, lawful basis, explicit consent, vendor access, retention, rights, withdrawal, complaints, and age checks. Address storage, human review, training, memory, and cookies separately. Explain what happens if users don’t provide information. Provide consent information before asking for consent.
For indirectly collected data, include the data categories and sources. Give notice within the Article 14 deadline - normally no later than one month, or earlier at the first communication or disclosure.
AI and Data Privacy Explained | GDPR, AI Act & Compliance Guide
Conclusion: GDPR Checklist for Adult AI Chats
Use this checklist to check the controls described above - not to prove compliance. Document each control, including purposes, lawful bases, special-category handling, records of processing, and consent logs.
Run a Data Protection Impact Assessment (DPIA) before processing high-risk intimate chats. Assess whether large-scale sensitive-data processing requires a data protection officer (DPO). Treat BDSM and fetish preferences as special-category data, with explicit consent and stronger safeguards.
Check 18+ verification, vendor contracts, international-transfer safeguards, encryption, and access controls. Test retention, deletion, and rights-request workflows. Keep a breach plan that covers notifying authorities within 72 hours where required and notifying users without undue delay where required.
Reassess before changing models, memory, vendors, processing locations, or processing purposes. After each change, update processing records, risk assessments, consent flows, and notices.
FAQs
Does GDPR protect my chats with a US-based operator?
GDPR applies when a US-based operator offers services to people in the EU/EEA or otherwise falls under EU data-protection jurisdiction. If you’re in the US and use a US-based operator, GDPR generally won’t govern your chats.
The sources discuss AI Mistress’ privacy approach in the context of GDPR, but they don’t establish that GDPR covers US users’ chats with a US-based operator.
Can I delete chats already used for AI training?
AI Mistress has a strict no-chat-history policy. It doesn’t store your conversations, so there are no saved chats to delete, use for AI training, or recover later. Sessions run on German servers under GDPR, and your interactions leave no stored digital trace on the platform.
What can I do if my deletion request is ignored?
Check the privacy policy for data retention and deletion procedures. Look for a dedicated process to remove or report content, too. If the service doesn’t respond or gives unclear answers about your rights, assume it may still have access to your information.
AI Mistress follows strict GDPR requirements and a no-chat-history policy. It doesn’t store sessions on its servers, so there’s no persistent chat data to recover or delete.